QA Testing Services for SaaS Startups: How Vervali Works
How Vervali tests a SaaS startup's product: what to test first, when to outsource, manual or automation, the monthly cost at published rates, and how the free pilot…
Stay ahead of cybercriminals by identifying and addressing social engineering vulnerabilities in your business operations. Vervali runs authorised phishing, pretexting and impersonation tests inside written rules of engagement, then gives you a risk-ranked report, training priorities and a retest.
ISO/IEC 17025:2017Accredited testing laboratory
CMMI Maturity Level 3The process is written down and repeats
ISO 9001:2015Quality management

ISO/IEC 27001Information security
Your people are the front door attackers try first. We test how they respond before a real attacker does.
Realistic email campaigns that measure who opens, clicks, enters credentials and, just as important, who reports it to your security team.
Phone and message scenarios where testers pose as IT, vendors or executives to see whether staff hand over access or data.
Attacks built around your structure, culture and public footprint, including baiting and impersonation of trusted people.
Your firewall cannot stop an employee who trusts the wrong email.
Free Exposure CheckThe human gaps that bypass every technical control you paid for.
Staff who open links or attachments from senders they have never verified.
Logins entered on lookalike pages or shared over the phone with a convincing caller.
Help desks and finance teams that act on requests without checking who is asking.
Suspicious messages nobody reports, so the security team never hears about them.
Attackers strike when your defences are in flux. Test during the changes that open gaps: new hires, audits and post-training checks.
New staff, new reporting lines and new vendors are the gaps attackers look for first.
PCI DSS, HIPAA and ISO/IEC 27001 programmes expect evidence that awareness works. Technical testing runs through penetration testing.
A retest shows whether awareness training changed behaviour, not just attendance records.
Security engagements where verified, risk-ranked findings and retests closed real gaps.
Bank · VAPT and audit evidence
Before: vulnerability noise was burying the work that mattered, fixes took over 40 days and audit preparation took five days. After: 68% less vulnerability noise, time to fix under 16 days, audit preparation down from 5 days to 5 hours, and high-risk findings closed 3.5 times faster.
68% less vulnerability noiseTime to fix under 16 daysAudit prep 5 days to 5 hours3.5x high-risk closureInfrastructure VAPT across the exposed surface of a digital recharge and payments platform, with findings retested after remediation.
Web and infrastructure security testing for a global marine technology organisation, against the agreed in-scope assets.
API and network exposure testing on a fintech platform, with risk-ranked findings for the engineering team.
End-to-end security testing across the agreed in-scope product of a SaaS gaming platform, with a retest after fixes.
From a target list to a trained team, 9am to 1pm Eastern with delivery from India.
Name the Targets
Tell us the teams, roles and channels in scope: email, phone, messaging or on site.
Agree the Rules
We sign rules of engagement naming scenarios, limits and test windows, then quote.
Run the Campaign
Testers run the agreed scenarios and record every response, click and report.
Report and Retest
You get a risk-ranked report and training priorities, then we retest after training.

OUR BLOGS
How Vervali tests a SaaS startup's product: what to test first, when to outsource, manual or automation, the monthly cost at published rates, and how the free pilot…
Vervali offers test automation as a service: framework, suite, CI integration and maintenance on a monthly allocation, from India with a 9am to 1pm Eastern overlap.
Vervali publishes what Shopify and ecommerce testing costs: hourly rates by role, monthly billing for a dedicated tester or retainer, a fixed price for a pre-peak lo…
Every path through a use case becomes at least one test case. A worked bank-transfer example shows the test table, and ISTQB's 2023 and 2025 syllabus changes explain…
What a soak test is, how it differs from load, stress and spike tests, how long to run it, the metrics that decide a pass, and how JMeter, k6 and Gatling hold a load…
This software testing checklist groups every item by the phase of the test process it belongs to, marks the items teams routinely skip, and shows how to wire the lis…
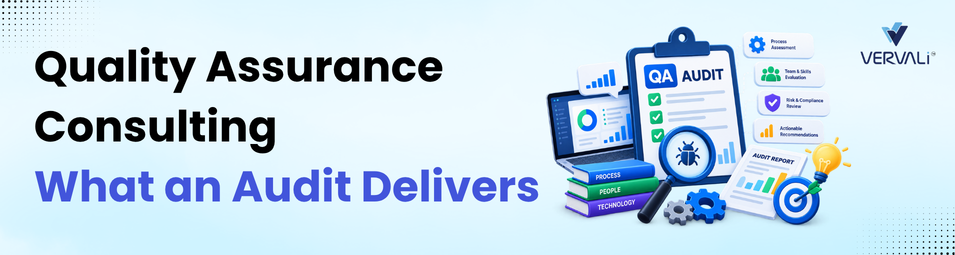
This guide explains what a QA maturity assessment scores you against, what the deliverable looks like on the last day, and when advisory work is the wrong purchase.
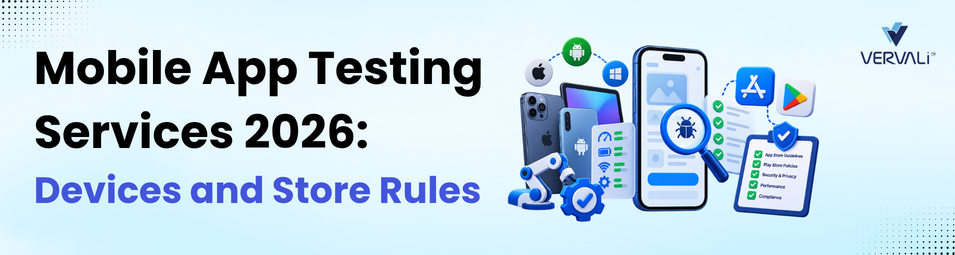
This guide explains what mobile app testing services cover, how to size a device matrix from United States traffic data, and what Apple and Google check before a rel…
Our Expertise


Trusted by 150+ Leading Brands

A Strong Team of 275+ QA and Dev Professionals

Worked across 450+ Successful Projects
 Email Us
 Call Us
From flawless code to flawless quality - we design, develop, and test digital solutions that deliver real results.